App Registration for Azure Connectors
Introduction
To enable ManagementStudio connectors to access data within Azure, an App registration must be created in Azure Active Directory. The App registration defines the permissions and access rights granted to ManagementStudio. It is recommended, though not required, to create a separate App registration for each connector used.
Creating an Azure App Registration
- Open the Azure portal.
- Navigate to
App registrations. - Select
New registration.- Enter a name, such as
ManagementStudio AAD Connector. - Choose
Accounts in this organization only. - Leave the Redirect URI blank.
- Enter a name, such as
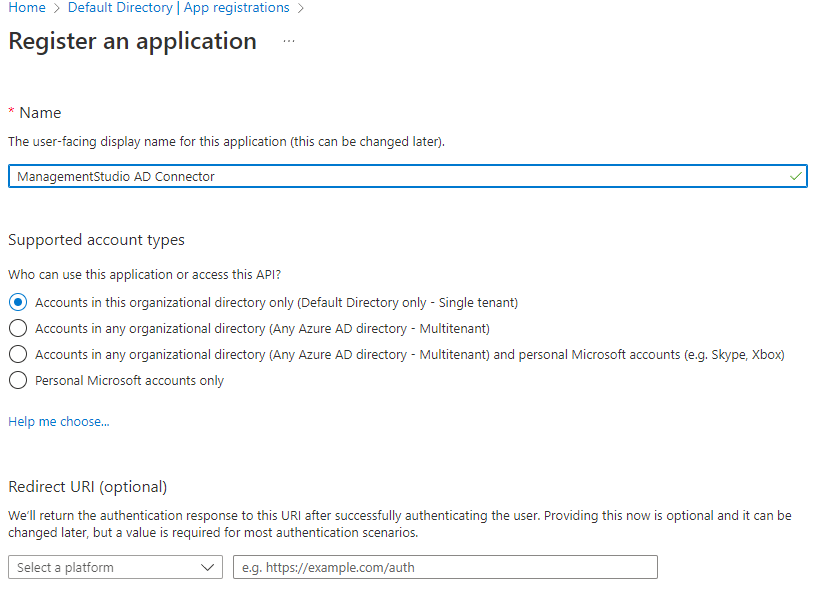
- Click
Register.
Authentication and Permissions
The required configuration varies depending on the authentication method selected: User/Password or Client Secret.
Auth: User/Pass
- Authentication
- Enable
Enable the following mobile and desktop flowsby setting it toYes. - Save the settings.
- Enable
- API Permissions
- Add permissions as
Delegated permissions. - Refer to the lists in the Permissions section.
- Grant admin consent for the added permissions.
- Add permissions as
Auth: Client Secret
- Certificates & Secrets
- In the left navigation, select
Certificates & secrets.
- In the left navigation, select
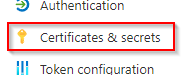
- Click
New client secret.
- Click
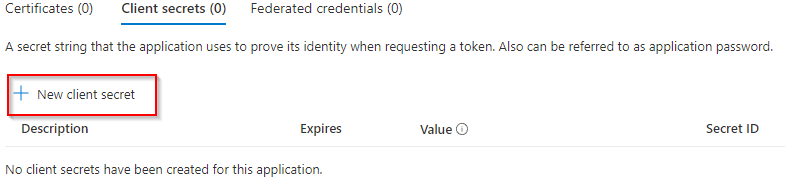
- Provide a name (e.g.,
ManagementStudio Secret). - Set
Expiresto24 months(for ENGAGE assessments, set to1 week).
- Provide a name (e.g.,
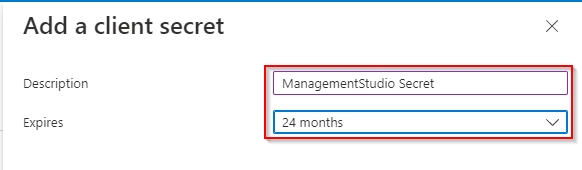
- Click
Add. - Important: Record the secret
Valueimmediately. The value is displayed once and cannot be retrieved again. - API Permissions
- Select
API permissionsin the left navigation. - Add permissions as
Application permissions. - Refer to the lists in the Permissions section.
- Select
- Click
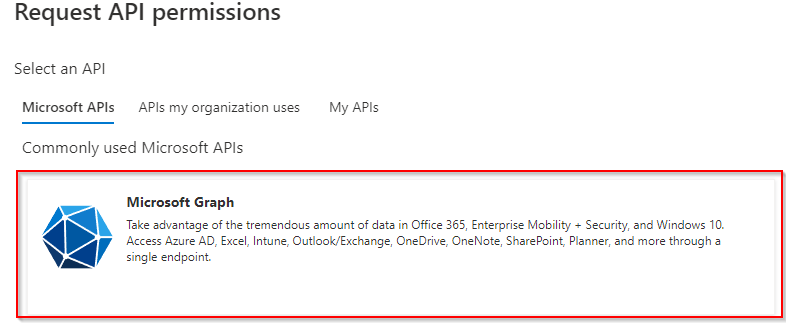
- Click
Add permissions. 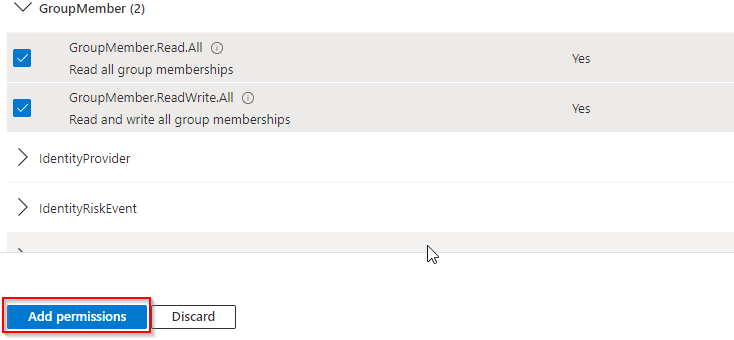
- Grant admin consent for the added permissions.
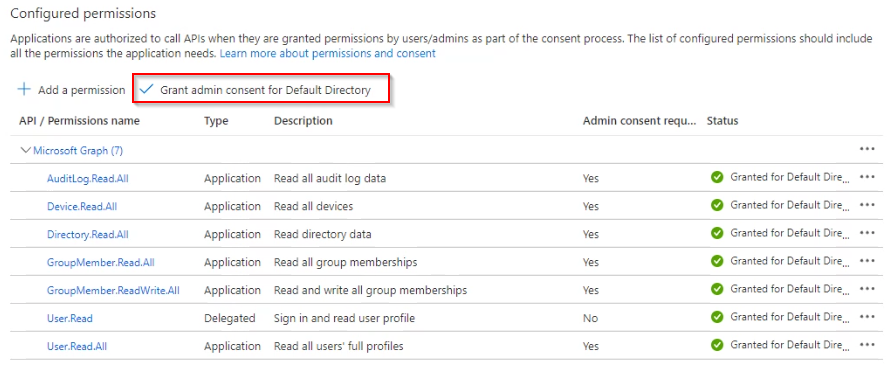
- Collect Required Information
- Go to
Overview. - Copy the
Application (Client) ID. - Copy the
Directory (tenant) ID. - Use the secret
Valuesaved earlier.
- Go to
- Click
Permissions
Azure AD Connector
Required Microsoft Graph Permissions
| Section | Permission | Note |
|---|---|---|
| Directory | Directory.Read.All | |
| User | User.Read.All | |
| Device | Device.Read.All | |
| AuditLog | AuditLog.Read.All | Optional: Required to retrieve users' last login time |
| GroupMember | GroupMember.Read.All | |
| GroupMember | GroupMember.ReadWrite.All | Optional: Allows ManagementStudio to add/remove items from Azure Groups (not required for ENGAGE assessments) |
Intune Connector
Required Microsoft Graph Permissions
| Section | Permission | Note |
|---|---|---|
| DeviceManagementApps | DeviceManagementApps.Read.All | Read Microsoft Intune apps |
| DeviceManagementManagedDevices | DeviceManagementManagedDevices.Read.All | Read Microsoft Intune devices |
| Directory | Directory.Read.All | Read AD directory data |
SMTP Email Send / Receive
Note: Only delegate access is supported for these permissions.
Required Microsoft Graph Permissions
| Section | Permission | Note |
|---|---|---|
| OpenId permissions | ||
| OpenId permissions | offline_access | |
| POP | POP.AccessAsUser.All | |
| SMTP | SMTP.Send |
Azure Email API
Required Azure Email API Permission
| Section | Permission | Type | Note |
|---|---|---|---|
| Mail.Send | Application | Allows ManagementStudio to send emails as another account (e.g., a project mailbox) |
Single Sign-On
Required Microsoft Graph Permission
| Section | Permission | Note |
|---|---|---|
| User | User.Read |
Was this article helpful?
That’s Great!
Thank you for your feedback
Sorry! We couldn't be helpful
Thank you for your feedback
Feedback sent
We appreciate your effort and will try to fix the article